You installed that AI summarizer to save 20 minutes per day on charting. Your scribe plugin writes perfect notes. The dictation extension transcribes patient visits in real time. Super convenient.
It's also a HIPAA breach waiting to happen.
Most physicians think their IT department has their browser locked down. They don't. I've walked into clinics where providers had 14 active Chrome extensions running on the same browser they use for Epic, Cerner, Athenahealth. Grammarly. Merlin. ChatGPT for Gmail. Two different AI note-takers fighting for DOM access. Every single one with permission to read everything you see.
Before you dive into new tools, ensure you understand how hospitals evaluate AI clinical tools before buying to avoid choosing vendors without proper security protocols.
This is the gap no one talks about because no one owns it.
This article is for educational purposes only and is not financial advice, not legal advice, and not tax advice. Implementation costs and legal exposure figures vary significantly by practice and vendor. Consult a qualified professional before changing your security posture.
The Invisible Leak: Why Browser Extensions are Your Clinic's Weakest Link
Here's the ugly truth: your hospital's firewall is excellent. Your EHR is encrypted. Your email has multi-factor auth. And none of that matters if your browser is a sieve.
I call it the "browser-in-the-middle" problem. You are sitting inside your secure EHR session, which you accessed through all the right security layers. But your browser extensions are also sitting inside that same session. They live inside your browser window.
IT security teams are wired to think perimeter defense. They secure the castle walls - network, servers, EHR login, VPN. Endpoint browser hygiene? That's usually an afterthought, delegated to a generic acceptable-use policy no one reads. Your IT team won't tell you about it because they aren't actively monitoring it. They don't have a dashboard showing "Dr. Smith's ChatGPT plugin scraped 400 patient records today."
The cost isn't abstract. If an extension exfiltrates PHI, even unintentionally, you are liable. Not the extension developer. You. The covered entity. Willful neglect? Start at $68,000 per violation. And the Office for Civil Rights doesn't care if you thought the plugin was "just helping with grammar."
The legal standard is simple: if you can see PHI on your screen, and you installed software that can also see it and send it somewhere else, you created the exposure. Intent doesn't matter.
The Anatomy of a Plugin Exfiltration: How Data Actually Leaves Your Office
Before finalizing your choice, ensure you weigh the financial and legal considerations of AI scribe adoption to align with practice goals.
Always ensure you are mastering healthcare data security by reviewing these key insights for medical professionals.
Let's fix this, but first, you need to understand how it actually happens. It's not hacking. It's exactly how these tools are designed to work.
1. The Permission Trap: "Read" vs. "Read and Change all your data on all websites"
When you click "Add to Chrome," you click past the permission box. Stop doing that.
"Read" sounds passive. It isn't. "Read and Change All Your Data On All Websites" means the extension can inject JavaScript into every tab you open. That includes your EHR tab. It can read the Document Object Model - the raw HTML of the patient chart - copy it, modify it, and transmit it.
I've seen physicians approve this for a simple AI writing assistant that promised to "improve clinical emails." That permission gave it access to everything. Everything.
2. How DOM scraping beats encryption every time
If you are concerned about technical hurdles, learn how to handle AI tool misunderstandings safely to maintain your confidence.
Your EHR encrypts data in transit. Great. Useless here.
The extension isn't intercepting network traffic. It's scraping the DOM after your browser has decrypted it for display. You log in, the EHR decrypts Mrs. Johnson's labs and history so you can read them. At that exact moment, the extension reads the same pixels you do. Then it packages that text and sends it to its own server for AI processing.
This is why your IT department's encryption audit shows "all clear." The data left after decryption.
3. Third-party API keys are a backdoor you can't see
Many AI plugins are just wrappers. The developer got an OpenAI or Anthropic API key and built a Chrome extension around it. Your patient data goes: EHR tab -> Extension -> Developer's server -> OpenAI API. That's two external hops you never authorized, with no Business Associate Agreement.
4. Case study: The transcription plugin problem
Real example from last year. A primary care group in the Midwest used a popular browser-based transcription plugin for patient encounters. It worked directly in the browser, listening via the microphone permission. The problem? To provide "smart summaries," it was also scraping the chief complaint and vitals from the DOM and bundling it with the audio transcript to a non-HIPAA-compliant transcription API offshore.
No one knew until a privacy officer noticed network traffic to an unknown domain during clinic hours. That one plugin triggered a full breach risk assessment for 3,200 patients.
That diagram is your entire risk in four boxes.
The Security Audit Protocol: A Step-by-Step Fix
Enough doom. Here's how you actually fix it today. This is the 30-minute audit I make every new practice do.
Step 1: Run the dirty inventory (5 minutes)
In Chrome, type chrome://extensions/ in your address bar. In Edge, edge://extensions/. Turn on "Developer Mode" toggle in the top right. Now you can see everything.
Screenshot the list. You'll be shocked. Delete anything you didn't actively install in the last 3 months. If you don't recognize it, remove it. Now.
Pay special attention to:
- Any AI writing, summarizing, scribe, or transcription tool
- Grammar/spell checkers
- Coupon finders, screenshot tools, PDF converters - classic data leakers
Step 2: Kill "Read and Change All Data" (10 minutes)
For every extension you keep, click "Details." Look at "Site access."
If it says "On all sites," that's a hard fail. Change it immediately to "On specific sites" or "On click." If the extension won't function without "all sites" access, delete it. Period. No AI email helper is worth universal access to your EHR.
If you use Epic Hyperspace in a browser, Cerner PowerChart, Elation - your EHR domain should never be in an AI plugin's allowed list unless it is IT-approved and BAA-covered.
Step 3: Demand a whitelist policy from IT (Your script)
Stop asking IT "is this plugin safe?" That puts the burden on you. Flip it.
Email your IT security officer this:
"We need a formal browser extension whitelist/blacklist policy for clinical workstations. I am requesting: 1) An approved list of AI tools with signed BAAs, 2) Browser Group Policy that blocks installation of non-whitelisted extensions, 3) A separate Chrome profile for clinical vs. non-clinical browsing."
That language forces action. Group Policy or tools like Chrome Enterprise can actually enforce this in 10 minutes of IT work. Most IT teams just haven't been asked.
Step 4: Sandbox your browsing
Fix that will save you tomorrow: Create two Chrome profiles.
Profile 1: "Clinical" - Only EHR, UpToDate, and IT-approved tools. Zero AI plugins. Profile 2: "Everything Else" - Your AI toys, Gmail, research. Never open the EHR in this profile.
Two clicks to switch profiles. 100% separation of patient data from consumer-grade AI. This is the single easiest win.
Step 5: Govern your APIs
If you love an AI tool, stop using the browser version. Ask the vendor: "Do you offer an enterprise API integration with a BAA that runs server-side, not via DOM scraping?" If the answer is no, it's not a clinical tool. It's a consumer toy.
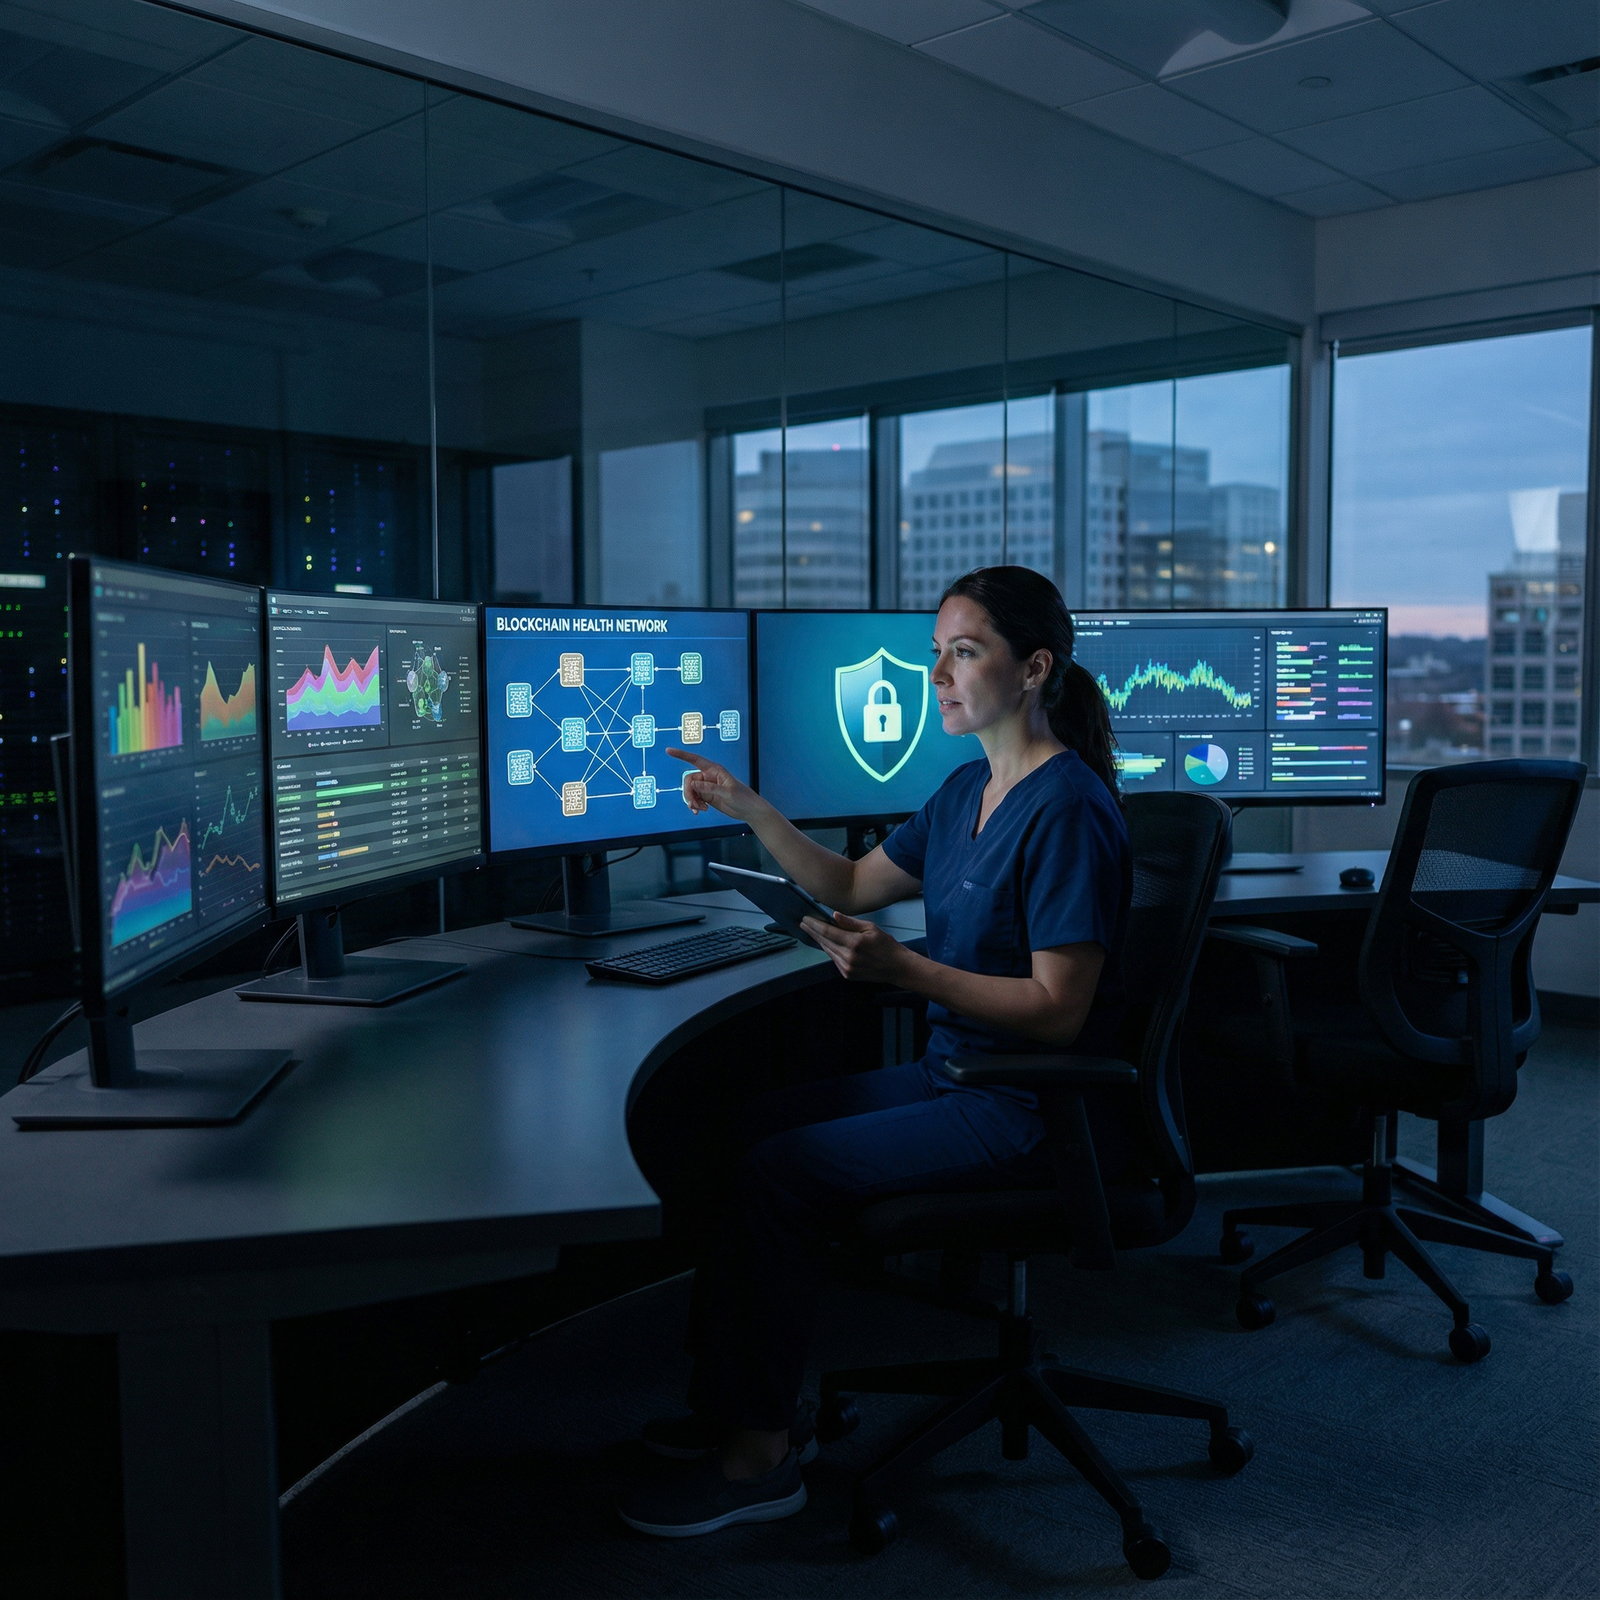
Comparative Risk Matrix: Native Tools vs. Plugin-Based AI
Not all AI deployment is equal. You have choices, and the risk delta is massive.
Consumer plugins are fast, free, and dangerous. Enterprise-integrated tools take longer to get approved but keep data sovereignty. Localized desktop AI is the gold standard for privacy but costs more.
Look at it bleakly:
- Consumer Plugins (Risk 9/10): Data leaves your machine, goes to an unknown server, often offshore, no BAA. You're betting your medical license on a privacy policy you didn't read.
- Enterprise Integrated API (Risk 4/10): Think DAX Copilot integrated natively into Epic, or Nabla that EHR embedded with BAA. Data stays in the BAA-covered pipeline. Audited. Loggable. This is where you want to be.
- Localized Desktop AI (Risk 2/10): AI model runs locally on your machine or private secure VPC. Nothing leaves. Fastest, most private. Companies like Abridge and Heidi are moving this way. Harder to deploy, but almost zero exfiltration risk.
Trade-off is speed vs. sovereignty. If you need it now, use enterprise API. If you can wait, push for localized.
Taking Control: Your Action Plan for Secure AI Adoption
You don't have to be anti-AI to be pro-security. You just have to be deliberate.
Do this in the next 24 hours:
- Complete Step 1 and 2 above. Remove high-risk permissions.
- Create your two Chrome profiles. Move all patient work to the locked-down Clinical profile.
Do this in the next week: 3. Draft a one-page physician AI usage policy for your group. Simple language: "No browser extension may access EHR domains without a signed BAA and IT whitelist approval. All AI transcription must be via approved enterprise tools only." 4. Schedule 15 minutes with IT. Don't lead with fear. Lead with help: "I want to adopt AI safely without creating HIPAA exposure for us. Here's the whitelist approach I'd like to implement. Can you help me deploy it?"
That framing works. You're not complaining. You're solving their problem too.
Innovation and privacy aren't mutually exclusive. But convenience without governance is just a breach you haven't discovered yet.
Assume everything in your browser is visible to every extension. Because it is.
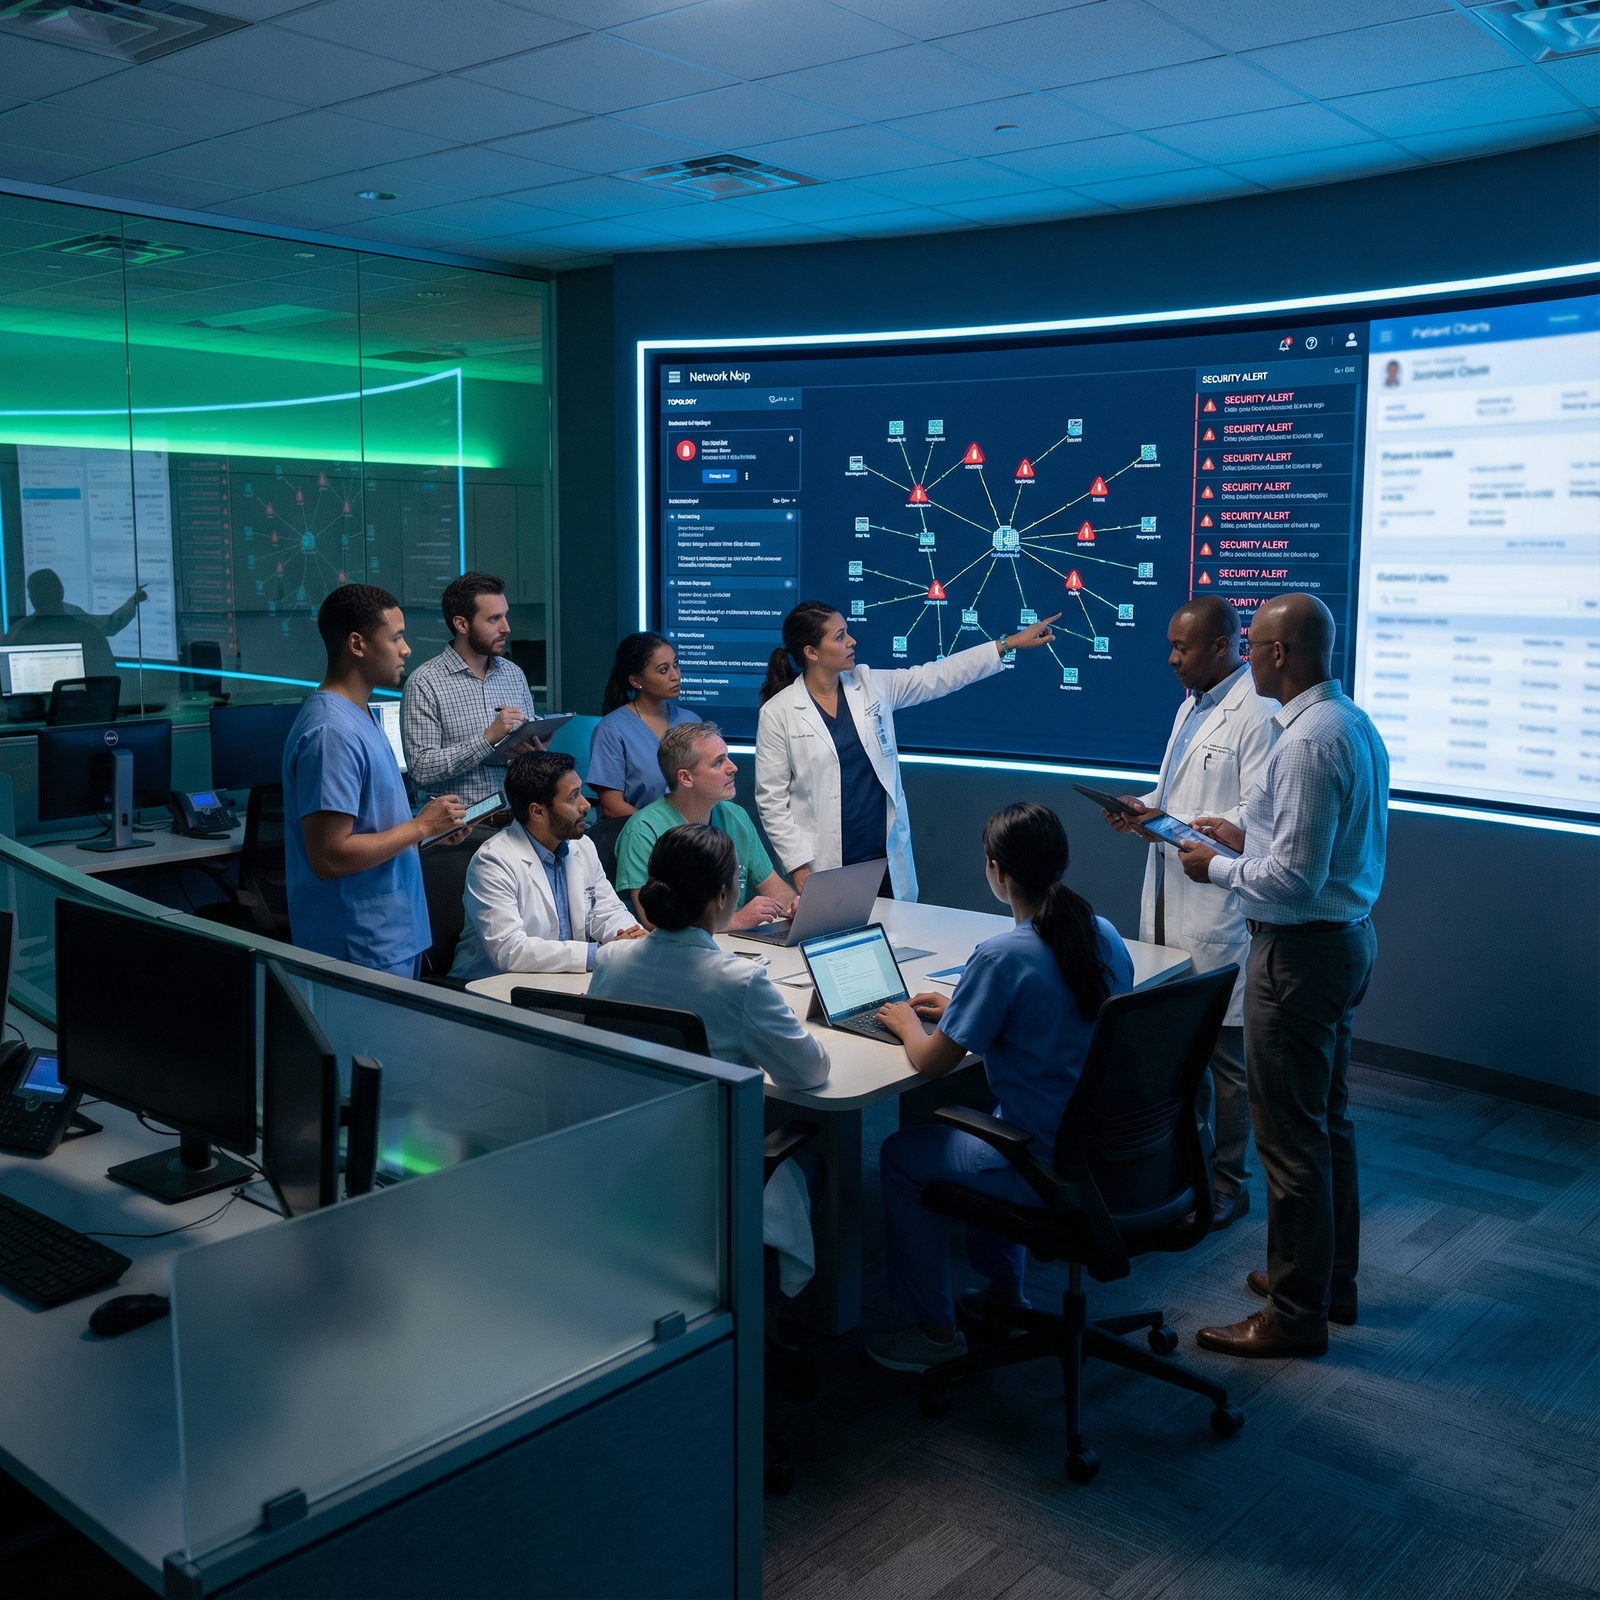
Key Takeaways
- Assume every AI plugin has access to the raw data visible in your browser window; if you can see it, the plugin can scrape it.
- Prioritize 'Domain Restricted' extensions that are verified by your IT department and covered under a Business Associate Agreement (BAA).
- Disable 'Read and Change' permissions for any non-essential browser extensions immediately to minimize the attack surface.
- The convenience of AI is not worth the risk of a HIPAA violation; always verify the data handling policy of the plugin developer.